
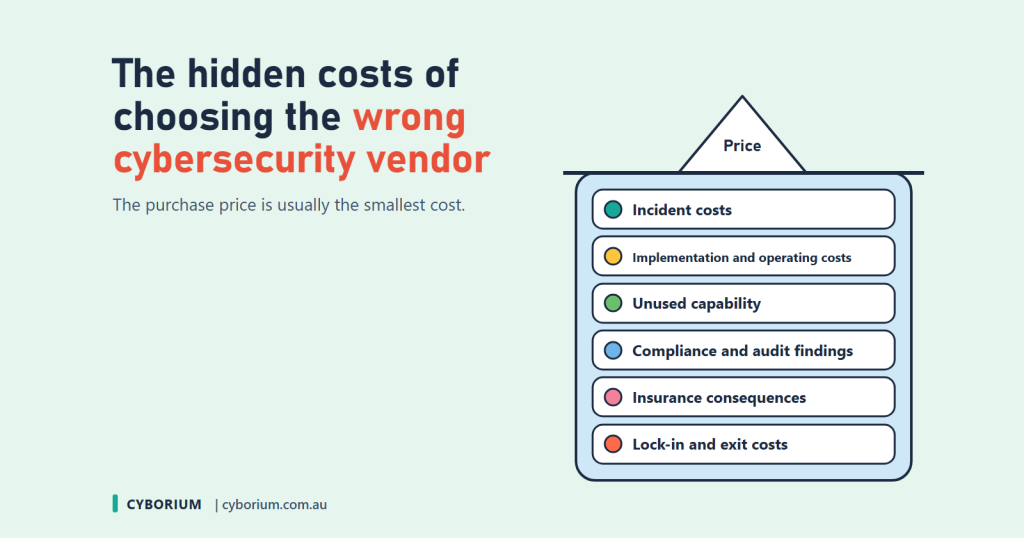
The purchase price is usually the smallest cost of choosing the wrong cybersecurity vendor. The larger costs arrive later and are harder to see in a business case. They include an incident the service did not detect or contain and months of effort to make the product work. They also include licences that go unused, audit findings, harder insurance questions and the cost of leaving a contract that no longer fits. Most of these costs can be anticipated during cybersecurity vendor selection in Australia, which is the cheapest time to avoid them.
CYBORIUM helps Australian organisations with cybersecurity vendor selection, covering products and services, through a structured vendor-neutral sourcing process. The selected provider pays CYBORIUM a capped fee. The client contracts directly with that provider, and CYBORIUM does not sell, deliver, operate or invoice the technology.
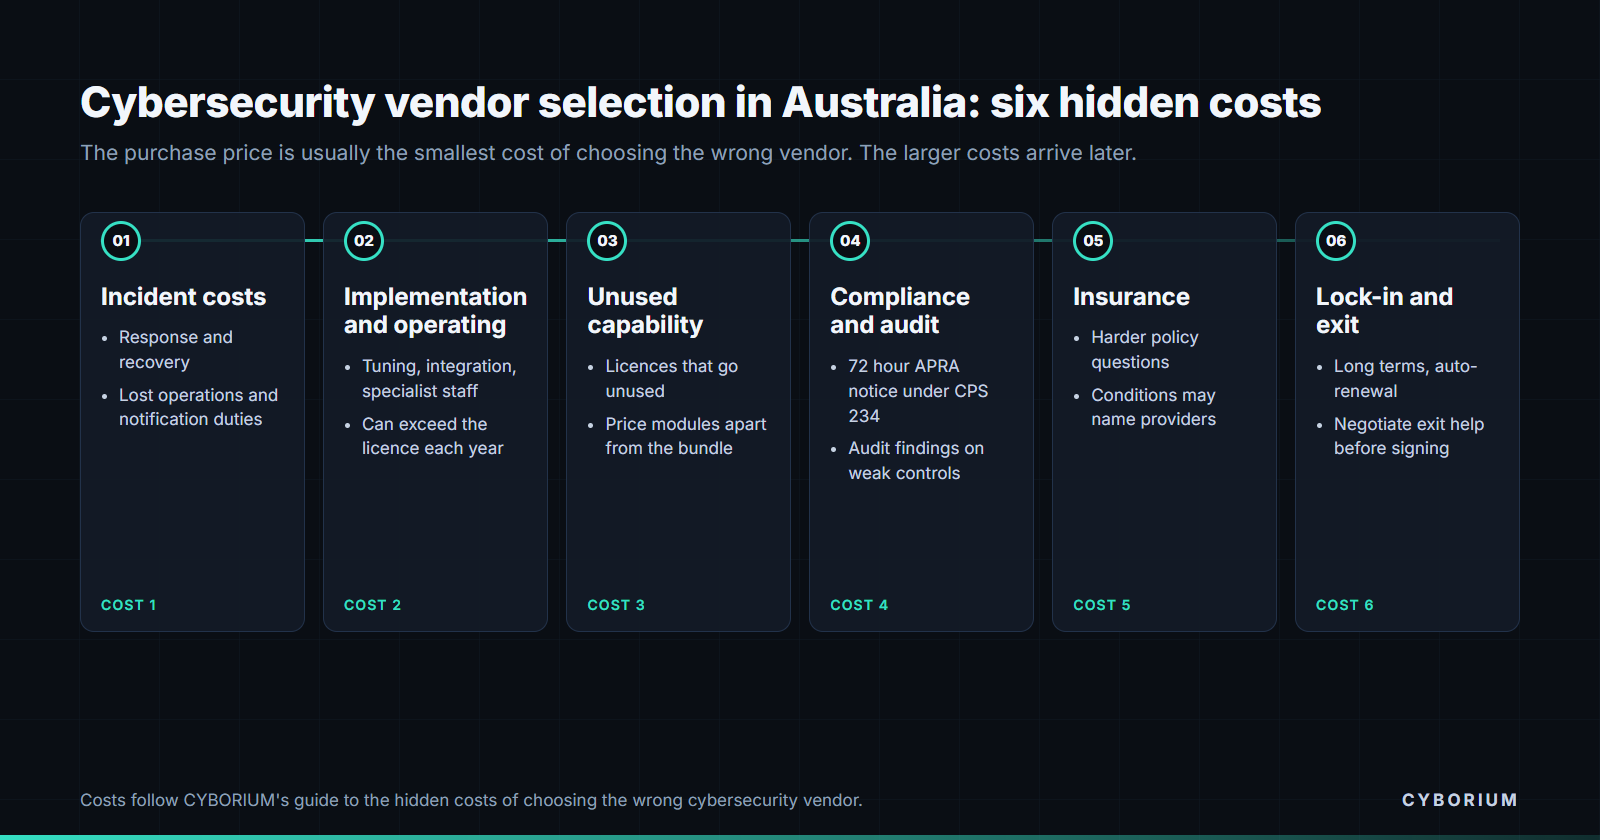
Incident costs
When a security product or managed service fails to detect or contain an attack, the organisation carries the cost. That covers response, recovery, lost operations and any notification obligations. ASD’s Annual Cyber Threat Report 2024-25 reported an average self-reported cost of $80,850 per cybercrime report for businesses. The cost for a serious incident at a larger organisation can be far higher.
How to reduce it during selection: test detection and response against scenarios relevant to your environment. Put response times and response authority in the contract rather than relying on a sales description.
Implementation and operating costs
A product that needs extensive tuning, custom integration or specialist staff can cost more to run each year than its licence. These costs rarely appear in a vendor proposal because they fall on the decision owner’s team or a separate integrator. CYBORIUM's technology TCO calculator adds exactly this kind of cost, including your own staff time, next to the vendor's quoted price over the full term.
How to reduce it: ask each vendor for the operating effort in hours per month, who performs each task. Also ask what the integration work involves for your tools. Include those costs in the comparison.
Unused capability
Security bundles and enterprise licence tiers often include modules that are never deployed. The organisation pays for them every year, and they can create a false sense of coverage in risk reports.
How to reduce it: price the components you will use in the first two years separately from the bundle. Also require a deployment plan that shows when each licensed module will be in production.
Compliance and audit findings
A vendor that cannot provide the right evidence can leave the organisation exposed in audits and regulatory reviews. For APRA-regulated entities, CPS 234 requires evaluating the information security capability of third parties. It also requires notifying APRA of material incidents within 72 hours, which depends on the provider notifying the entity quickly. Organisations handling personal information also need to meet Notifiable Data Breaches obligations.
How to reduce it: score security assurance, notification commitments and evidence access during evaluation, and settle them in the contract.
Insurance consequences
Cyber insurers ask detailed questions about controls such as multi-factor authentication, endpoint protection, backups and incident response arrangements. A control that exists on paper but is poorly implemented can make those answers harder to give accurately. Policy conditions may require specific providers or arrangements.
How to reduce it: check insurance requirements and panel arrangements before shortlisting, particularly for incident response and managed security services.
Lock-in and exit costs
Long terms, auto-renewal clauses, proprietary data formats and agents that are hard to remove make it expensive to leave a vendor that is not performing. The cost shows up at renewal, when the organisation has little bargaining power.
How to reduce it: negotiate exit assistance, data return in a usable format, termination for poor performance and renewal price caps. Do this while more than one vendor is still in contention.
Cybersecurity vendor selection checklist for Australia
- Detection and response tested against agreed scenarios in your environment.
- Operating effort and integration work estimated and included in the cost comparison.
- Components priced individually, with a deployment plan for each.
- Security assurance, notification times and evidence access settled.
- Insurance requirements checked.
- Exit, data return and renewal pricing agreed.
How CYBORIUM supports cybersecurity vendor selection in Australia
CYBORIUM can build these checks into the evaluation, coordinate vendors, model whole-of-life cost and support negotiation. The organisation keeps the decision and contracts directly with the selected provider. For a full method, see the cybersecurity vendor evaluation framework, and for the cost of getting advice itself, how procurement consultants get paid.
Updated 15 September 2026. This article is general information about cybersecurity procurement. It does not provide legal, insurance or regulatory advice.
Cybersecurity vendor selection standards for Australia
The cost of choosing wrongly in cybersecurity is partly commercial and partly regulatory. These cover both.
- ASD Annual Cyber Threat Report. Reported incident costs in Australia, including how they differ by organisation size.
- OAIC Notifiable Data Breaches. What a breach obliges you to do, on what timeline, regardless of which vendor was involved.
- APRA CPS 234. For regulated entities, the obligations that remain yours after a provider has failed.
Related from CYBORIUM
- Guided Vendor Evaluations
- Technology Market Expertise
- Cybersecurity Vendor Evaluation Framework for Australian Enterprises
- Managed Detection and Response Provider Evaluation for Australian Enterprises
- SOAR Platform Evaluation and Procurement Guide for Australian Enterprises
- Total Cost of Ownership for Technology Purchases
Which hidden costs are easiest to avoid?
Integration, training and exit costs. Ask for them in the quote, in writing, before you shortlist.
How do you put a number on a bad vendor choice?
Add the extra cost of fixing, replacing and migrating, plus the cost of time lost. Even a rough estimate shows why careful selection is cheaper.
Want a second opinion before you commit? Contact CYBORIUM or request a free market briefing.
Last updated:


