
Australian Cybersecurity Spending Statistics 2026: Market Size, Growth and Share of Global Spend
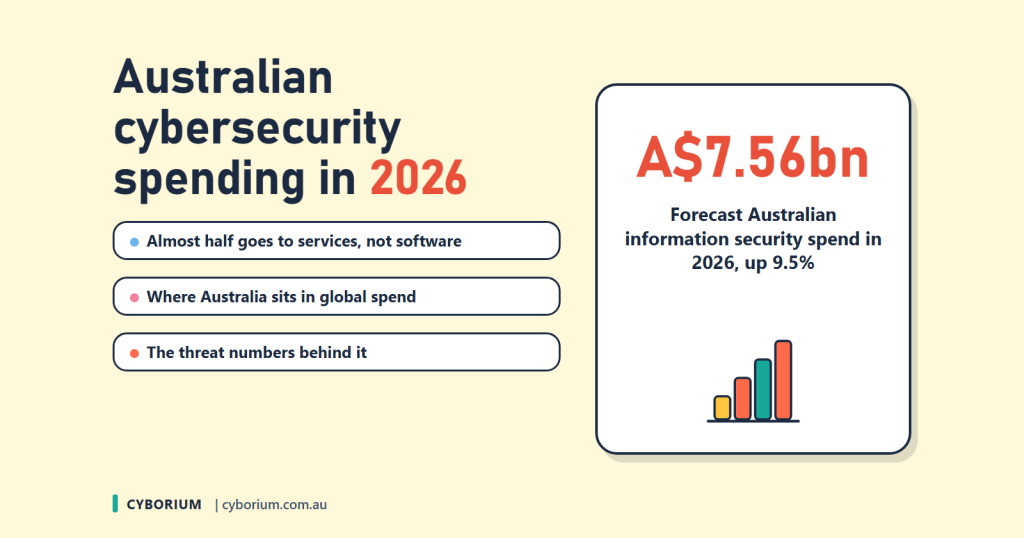
Australian organisations will spend A$7.56 billion on information security in 2026, up 9.5%. Market size by segment, security’s share of IT budgets, Australia’s share of global spend, and the ASD and OAIC threat figures behind it.
Secrets management procurement in Australia: buying for the credentials nobody logs into
Human administrators are the visible half of privileged access. The other half is machine credentials: API keys, database connection strings, service account passwords, certificates and tokens used by applications, pipelines and scripts. They outnumber human privileged accounts in most environments, they rotate less often, and they are the credentials most likely to be sitting in […]
OT and ICS security procurement in Australia: buying for environments that cannot be patched
Operational technology security is bought under a constraint that does not apply anywhere else in the security estate: you usually cannot patch the thing you are protecting, you often cannot reboot it, and in many cases you cannot scan it without risking the process it controls. Requirements written from an IT security template will fail […]
Email security procurement in Australia: what to require beyond the gateway
Email remains the most common way an attacker first reaches an organisation, and it is the control most often bought on brand rather than on requirements. The category has also changed shape. The secure email gateway that sat in front of the mail platform is no longer the whole answer, because most Australian organisations now […]
Backup and recovery procurement in Australia: buying for the day you need it
Backup is bought on capacity and judged on recovery. That gap is where most of the disappointment in this category lives. A platform can hold every byte an organisation has produced and still fail the only test that counts, which is bringing a named system back inside the time the business assumed it would take. […]
Privileged access management procurement in Australia: what to require from a PAM vendor
Privileged access is the smallest population of accounts in an organisation and the largest share of its risk. A domain administrator, a cloud root account, a service account with standing database rights: each one collapses the distance between an attacker landing on a workstation and an attacker owning the environment. Most Australian organisations already know […]
SBOM procurement in Australia: what to require from software providers
A practical six-point acceptance matrix for requiring current, complete and machine-readable software bill of materials evidence from technology providers.
What are the benefits of cybersecurity procurement services?
What a cybersecurity procurement service adds: comparable proposals, tested vendor claims, and contracts that hold up under audit.
Essentials for Enterprise IT: What Changes From the Essential Eight and What It Means for Contracts
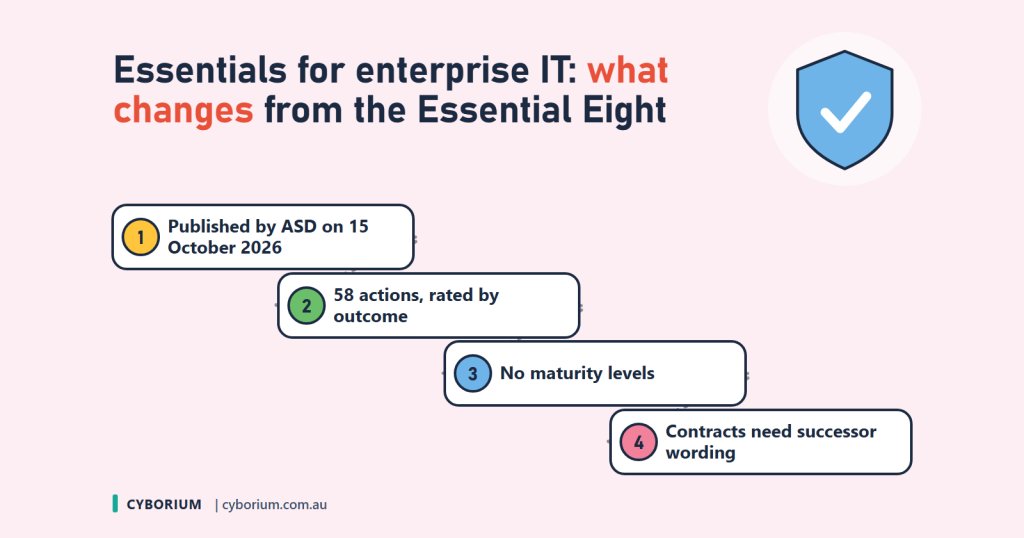
ASD published Essentials for enterprise IT on 15 October 2026: 58 actions, no maturity levels, and what it means for contracts and suppliers.
Cybersecurity Vendor Evaluation Framework for Australian Enterprises
A practical five-stage framework for Australian enterprises to define requirements, evaluate cybersecurity providers, test risk and compare commercial value.