
How to Shortlist IT Vendors Without Wasting Time or Budget
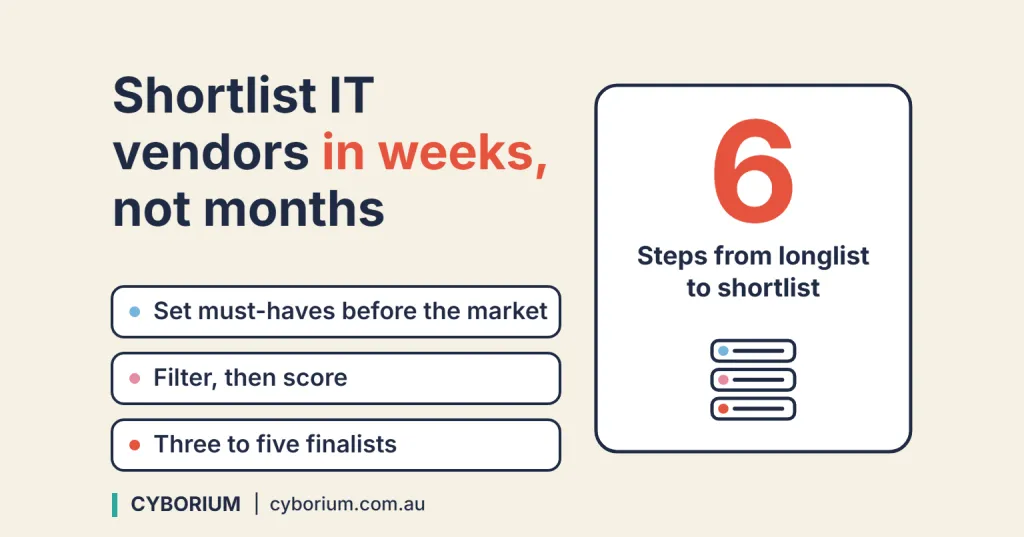
A six-step method for moving from a market-wide longlist to three to five credible IT vendors, quickly and defensibly.
Outsourcing procurement risks: ten failure modes and the control for each
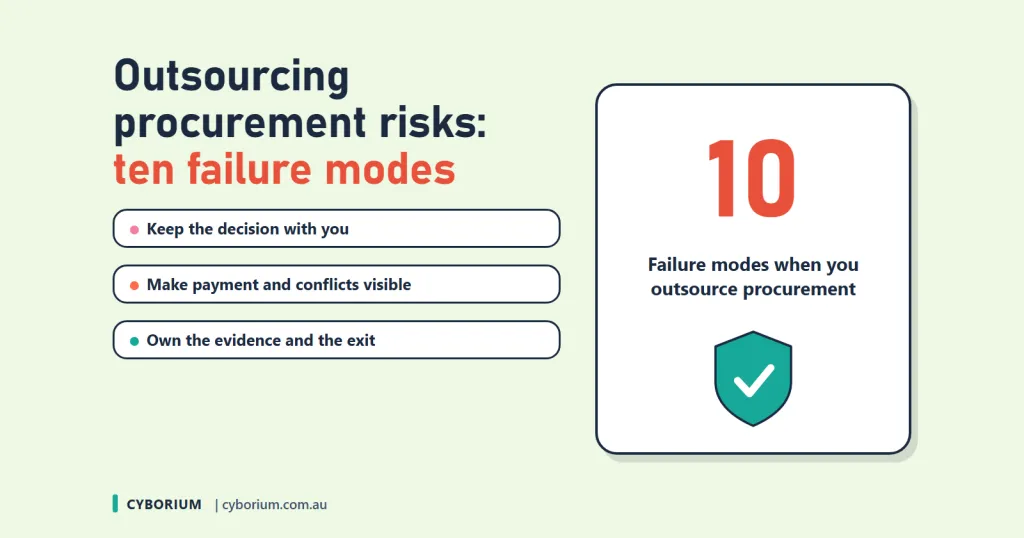
Ten outsourcing procurement risks and the control for each: knowledge, conflicts, decision rights, evidence, data, CPS 230, subcontracting and exit.
Information Security in Procurement: What to Require at Each Stage of a Technology Purchase
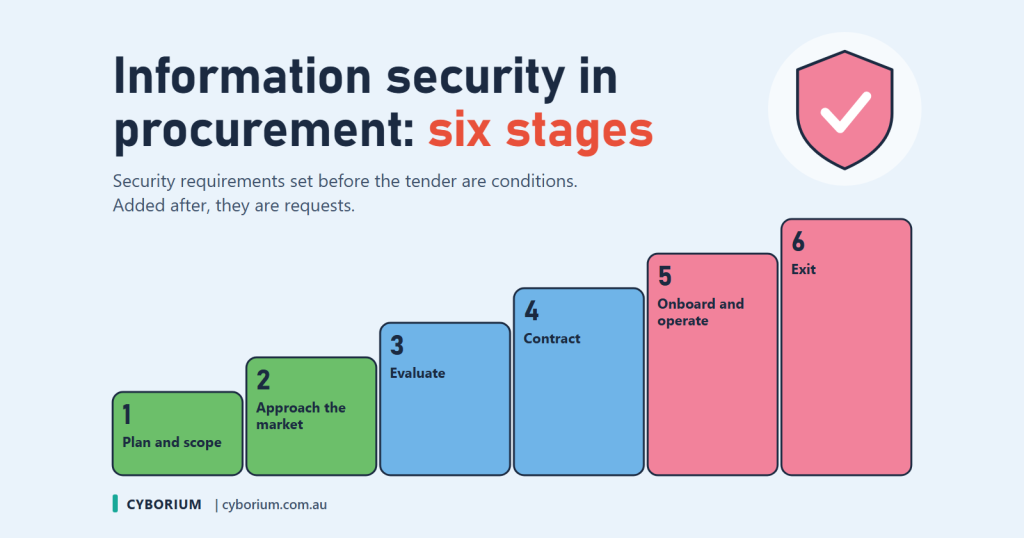
Security requirements added after a supplier is chosen are requests; added before, they are conditions. What to require at each stage of a technology purchase, with a contract checklist mapped to the Information Security Manual.
Exit and Transition-Out: What It Costs to Leave, and How to Price It Before You Sign
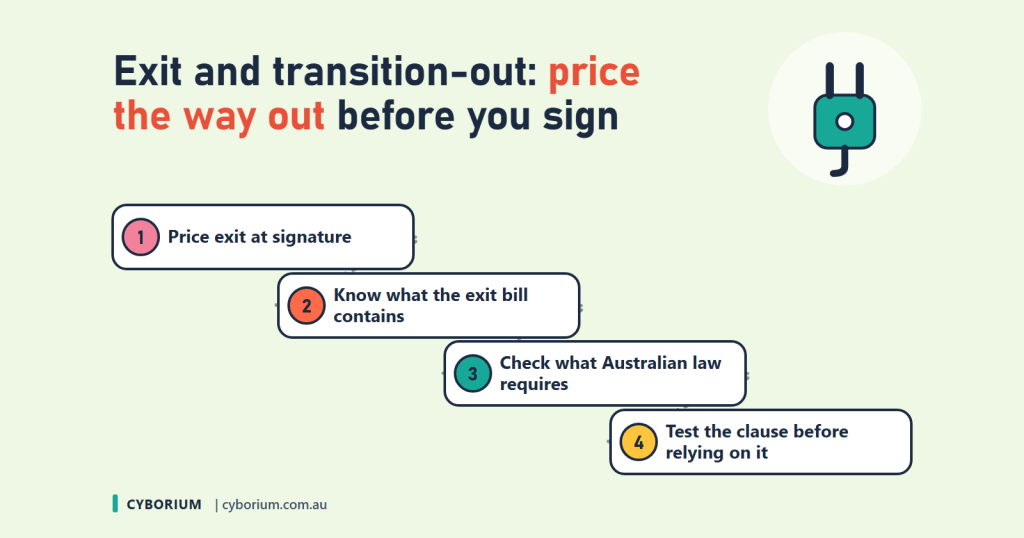
The price of leaving a supplier is set on the day you sign. The six components of an exit bill, what CPS 230 and the EU Data Act actually require, and the terms to negotiate before a preferred supplier is named.
Privileged access management procurement in Australia: what to require from a PAM vendor
Privileged access is the smallest population of accounts in an organisation and the largest share of its risk. A domain administrator, a cloud root account, a service account with standing database rights: each one collapses the distance between an attacker landing on a workstation and an attacker owning the environment. Most Australian organisations already know […]
Software licence renewals in Australia: running a renewal as a procurement event
Most enterprise software agreements are not lost in a competitive process. They are lost at renewal, in the six weeks before an expiry date, against a quote that arrived without warning and a vendor who knows exactly how little time is left. The purchase itself was governed. The renewal, which commits far more money over […]
How to manage procurement risk in IT and cybersecurity
Procurement risk is the risk that the buying process itself produces the wrong outcome: the wrong provider, the wrong scope, or a contract that cannot be defended later. It is distinct from delivery risk. A project can be run well and still fail because the decision that started it was made on incomplete information. What […]
How does independent IT vendor evaluation work?
How an independent IT vendor evaluation runs: defining criteria before the market is approached, scoring on evidence, and who pays the evaluator.
What is vendor due diligence?
Vendor due diligence explained: what gets checked before contract, how it differs from a security questionnaire, and what evidence to ask for.
What is third-party risk management?
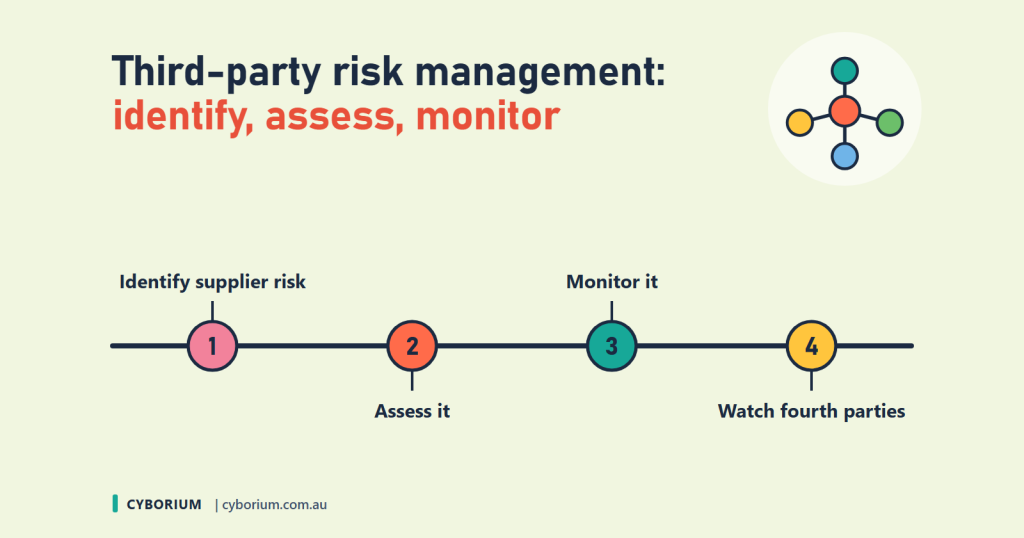
Third-party risk management explained: the lifecycle, why fourth parties matter, and how Australian regulation treats supplier oversight.