
Enhanced CIRMP Rules: What SOCI Supply Chain Obligations Mean for Vendor Procurement
The enhanced CIRMP Rules commenced 10 June 2026. What Australian critical infrastructure entities must now assess about their major suppliers, and by when.
Vendor and Supplier Risk Management for Enterprise Procurement
A structured vendor and supplier risk pathway for enterprise procurement. What is enterprise vendor risk management? Enterprise vendor risk management is the process of assessing and monitoring the risk a third-party supplier introduces to an organisation. It covers security posture, delivery capability, financial stability and exit terms, applied before contract is signed and repeated throughout […]
How APRA CPS 230 and CPS 234 Change Technology Vendor Selection
What APRA CPS 230 and CPS 234 require of regulated entities when they choose technology providers, and a selection process that produces the evidence both standards expect.
How to Evaluate Technology Vendors Without the Bias
Vendor selection is one of the highest-stakes decisions an enterprise buyer makes. This guide explains how to build a structured, bias-free evaluation process that produces defensible outcomes and keeps the buyer in control.
Vendor Management in Sydney: Five Problems and How to Fix Them
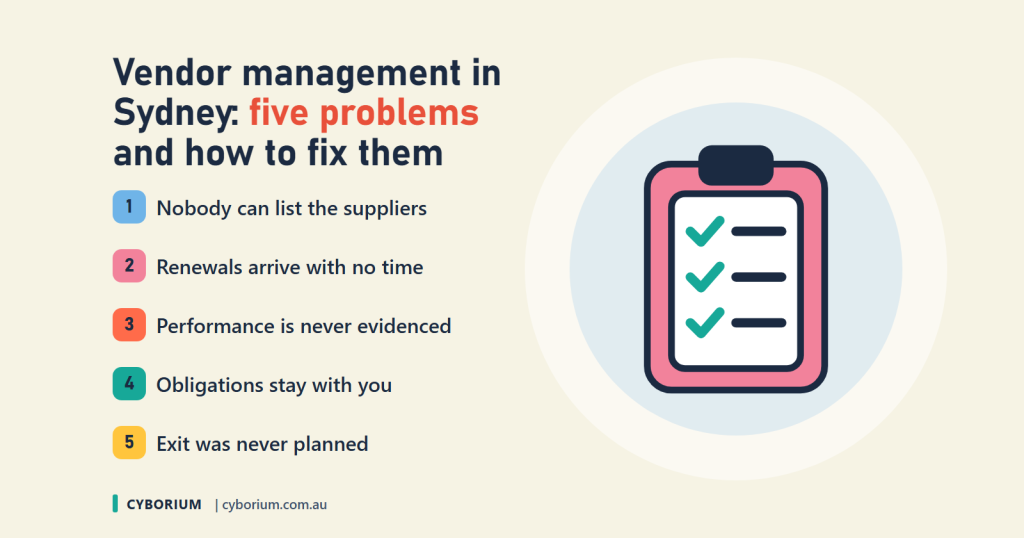
The five vendor management problems that show up most often in a review, from no supplier register to unplanned exit, each with a practical fix.
Cyber Risk Quantification: Evaluating Providers and Using Results in Insurance Decisions
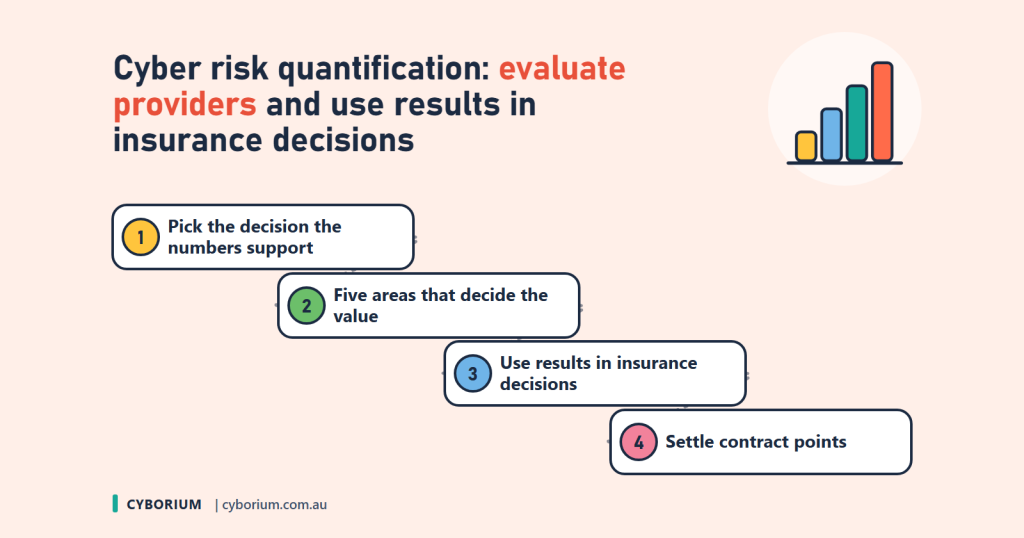
How to compare cyber risk quantification providers, check the inputs behind their loss estimates, and use the results in insurance and security investment decisions.